The difference between a chatbot and an AI agent is not how convincing the answer sounds, but what can happen after it. A chatbot explains. An agent can preserve the thread of a job, consult sources, call tools, prepare files and stop before an action that requires approval. OpenAI Agents API turns that idea into managed infrastructure that an application can use without rebuilding the entire orchestration mechanism from scratch.
This matters to businesses because it moves the question from “what text can the model generate?” to “what business outcome can the software achieve, within which limits and with what evidence?” A good answer is no longer the final product. The product is the complete path between request, data, tools, verification and outcome.
The essential point: Agents API does not give a company a ready-made “digital employee”. It gives developers an engine for durable work sessions. Rules, permissions, connections to company systems, approvals and accountability remain part of the application built around it.
An architectural change, not just another model
In a conventional AI integration, an application sends a prompt and receives a result. If the task has ten stages, the developer must preserve history, decide which tool comes next, handle failures and resume the process after an interruption. An agent adds a coordination layer above the model.
| System type | How it works | Where it fits |
|---|---|---|
| Chatbot | Answers questions and maintains a conversation | Support, guidance and information retrieval |
| Deterministic automation | Executes fixed steps under explicit rules | Invoices, notifications, synchronization and exact validation |
| AI agent | Selects and coordinates steps, tools and sources inside a bounded objective | Investigation, analysis, documents and variable processes |
An agent does not replace conventional automation. Most of the time, it uses it. If a rule can be expressed exactly in code, that step should remain deterministic. The model is valuable where context must be interpreted, alternatives compared or the next action selected from an allowed set.
What OpenAI Agents API actually provides
OpenAI's documentation defines four primary resources. Together, they explain the product more accurately than the broad word “agent”:
- The agent combines the model, instructions, tools and MCP connections, a standard way to use external services and data under controlled access.
- The execution environment is where it can run commands, work with files and produce artifacts. It may be an OpenAI-hosted sandbox, a company-managed environment or no environment at all when the task needs neither files nor compute.
- The session is the durable instance that preserves the work. It can contain several turns and continue after an answer or interruption without manually reconstructing the entire conversation.
- Events and items describe inputs, outputs, tool calls, states and results created during the work.
OpenAI manages the Codex harness that orchestrates the session, context compaction and recovery. The customer's application decides which task to submit, which model to use, which tools to expose and where code executes. That separation is useful: agent infrastructure can be managed without handing business logic to the model.
At the time of review, Agents API is a beta capability. It deserves serious evaluation, but interfaces, constraints and operating options may evolve. A pilot should be designed so that a provider or model can be changed without rewriting the whole product.
What a well-designed workflow looks like
Consider a quote request received by a company. A weak system sends the whole message to a model and then allows any action. A mature system separates the process into stages with different risk levels:
- The application validates fields, consent and user identity through conventional rules.
- The agent classifies the request and asks for more information only when relevant details are missing.
- A read-only tool retrieves approved services, availability and commercial rules.
- The agent prepares a summary and a proposal but does not send it.
- An employee sees the sources, assumptions and proposed changes, then approves or corrects them.
- Only after approval does a separate function write validated data to the CRM and send the message.
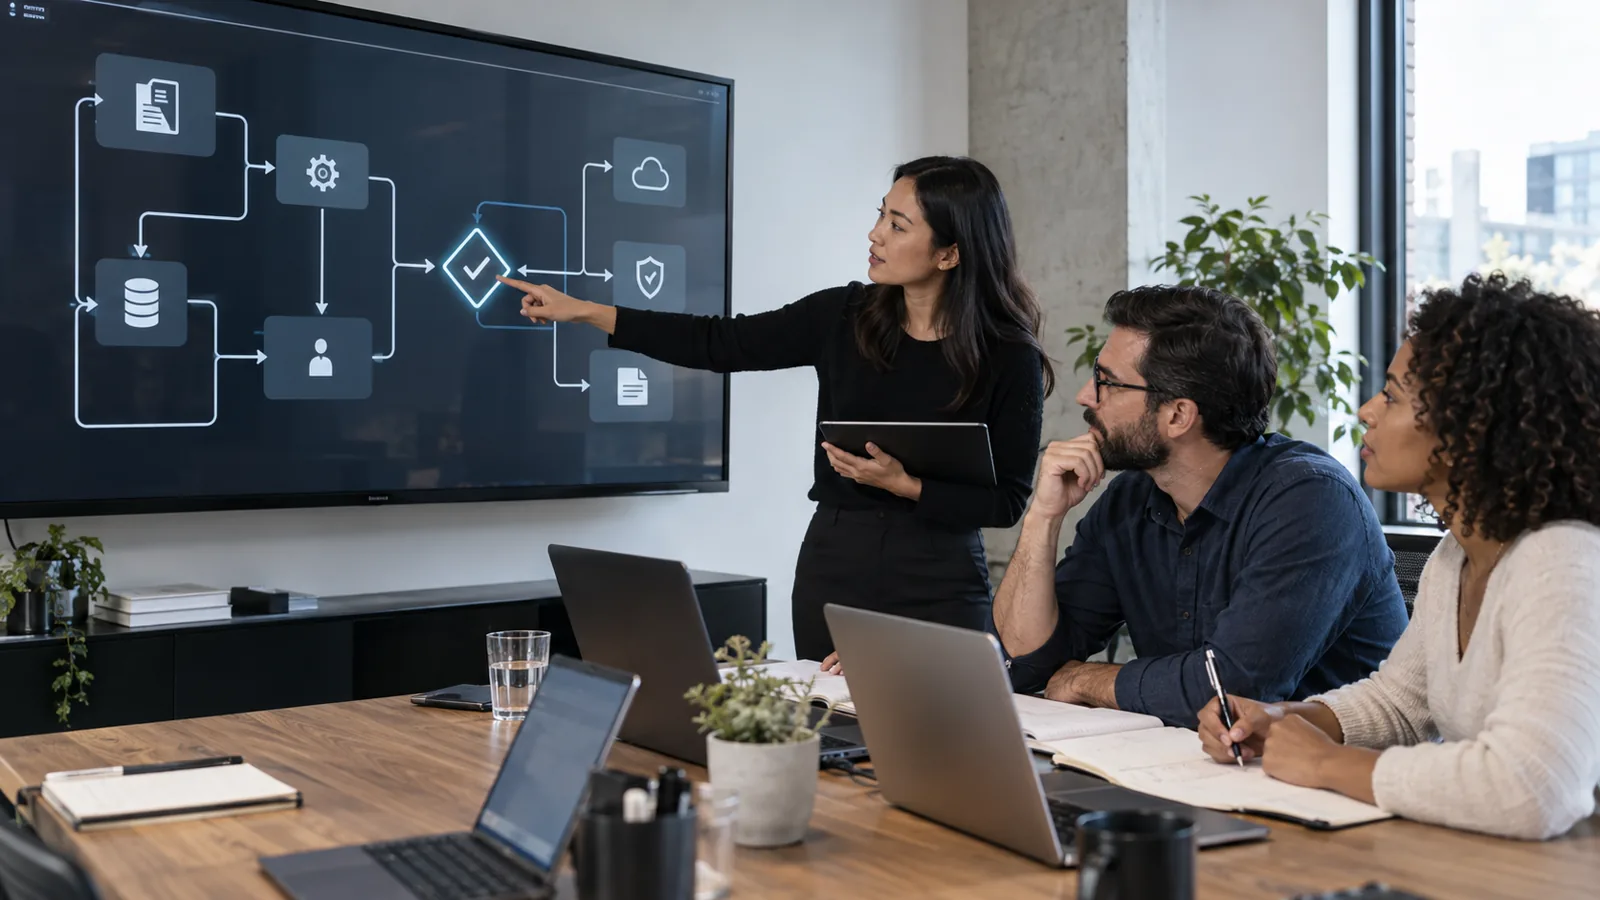
The decisive element is the function. In Agents API, an agent can request a function defined by the application, and the session can wait for the result. Company code executes the operation and returns the response. This is where validation, role-based permissions, value limits and human confirmation can be inserted. The model asks; the application decides whether the request is permitted.
Where it can create value inside a company
Requests, support and quoting
An agent can collect information from a conversation, identify intent, consult approved documentation and create a summary for the team. It shortens response time for straightforward requests. For ambiguous cases, it escalates the conversation together with its history and remaining questions instead of inventing an answer.
Documents without a uniform structure
Contracts, applications, reports or technical sheets can be read, compared with a requirements list and turned into structured output. The agent is useful when order and wording differ between documents. Final validation should still use rules and, for important decisions, a qualified specialist.
Analysis and reporting
An agent can query read-only sources, compare periods, flag anomalies and prepare explanations. It should not change budgets or accounting data simply because it detected a variation. Separating analysis from execution makes reporting faster without turning a hypothesis into an action.
Technical investigation
Logs, alerts and recent changes can be correlated during an investigation. An agent can reproduce an error in an isolated environment and propose a fix. Production deployment, data deletion or access changes should remain separate, audited and approved workflows.
These scenarios make sense when they belong to a coherent product. In custom applications with AI integration, interface, data and permissions are as important as the model. For repeated processes spanning several systems, business automation with AI integration can combine interpretation with exact rules. When the solution also needs accounts, dashboards, APIs and administration, the starting point remains custom software development, not prompt selection.
The first filter for European companies: data
An impressive feature cannot compensate for an unsuitable data architecture. OpenAI's documentation states that Agents API currently supports data residency only in the United States and is not eligible for Zero Data Retention, the regime under which eligible data is not retained after processing. Using a company-managed sandbox does not automatically change this because the session and orchestration remain API resources.
A Romanian or European business should answer these questions before prototyping:
- Which personal, commercial or confidential data enters the session?
- Can it be removed, masked or replaced by internal identifiers?
- Which retention period and processing region are contractually acceptable?
- Which providers and subprocessors appear across the full path?
- Can the use case work with synthetic data or read-only access?
If the answers are unclear, Agents SDK, Responses API or proprietary orchestration may be the right solution instead of Agents API. The choice should follow the product's data requirements, not the novelty of the technology.
The agent does not receive the keys to the building
An execution environment may give an agent access to files, network and credentials. Security therefore cannot be reduced to an instruction saying “do not perform dangerous actions”. OpenAI recommends isolated workloads, outbound access only to approved destinations and keeping the application key outside the environment where agent-generated code runs.
A prudent design includes at least:
- narrow tools, such as “retrieve customer by ID”, rather than general database access;
- least privilege and separation between reading, proposing and writing;
- isolated environments for users or customers that must not share data;
- approved network destinations, without open internet when the task does not need it;
- a credential broker for external services so the secret never reaches the sandbox;
- time, cost and step limits for every session;
- idempotent operations that do not duplicate an order or email when work resumes;
- an audit trail and procedures for stopping, cancelling and recovering work.
Multi-agent: an effective team or merely a larger bill?
Agents API can delegate work to subagents, each with its own context. They can run in parallel, while the primary agent combines their results. This is useful for independent work: separate reviews of three documents, simultaneous investigation of several hypotheses or distinct checks against the same dataset.
There is no value in splitting a process simply because the option exists. Dependent steps are easier to follow in the primary agent. Two subagents editing the same resource can conflict, and every additional context consumes time and tokens. A sound rule is simple: delegation should reduce elapsed time or measurably improve quality, not merely make the architecture look sophisticated.
The real cost is not the price of one answer
According to the documentation, model usage is billed at the selected model's API rate, OpenAI tools at their standard rates, and hosted sandboxes at container rates. One agent task may involve several model responses, tool calls, searches, subagents, execution time and retries.
The useful question is therefore not “how much does one million tokens cost?”, but “how much does an accepted outcome cost?” A cheaper model that repeats steps or creates many exceptions may cost more operationally than a stronger one. Likewise, a deterministic automation taking milliseconds is preferable to an agent for a simple rule.
| Metric | What it reveals |
|---|---|
| Cost per completed task | The full cost, including retries and tools |
| Escalation rate | How often the agent cannot decide within its limits |
| Human time saved | Operational value, not only model speed |
| Rejected or corrected actions | Proposal quality before execution |
| Incidents and incorrect actions | The real risk created by autonomy |
Traceability separates a demo from a product
Agents API preserves sessions, turns and items, while the tracing dashboard can show model responses, tool calls, results, duration and subagent activity. That helps diagnose failures and understand cost. It does not replace the application's audit log, because a business must connect an agent action to the user, role, version, business object and approval.
Tracing also has beta limitations. Recorded data should be treated as potentially sensitive, and the application's own observability should be designed around minimization and explicit retention. “We can see everything” is not a compliance strategy; the organization must decide what deserves to be recorded and who may inspect it.
A 30-day pilot that tells the truth
- Select one outcome. For example, one reviewed case file or a request summary prepared for a CRM.
- Build a test set. Include normal cases, missing information, contradictions, incorrect documents and attempts to manipulate instructions.
- Begin with read-only access. The agent may analyze and propose without changing external systems.
- Define thresholds. Which accuracy, time, cost and escalation rate justify the next stage?
- Add one controlled action. Validate arguments in code and require approval for financial, legal or reputational impact.
- Compare with the current process. Measure total human time, not only the AI response time.
- Preserve a simple exit. Work must continue manually when the service, model or integration is unavailable.
When Agents API is not worth using
An agent is a poor choice when the task has one predictable step, volume cannot justify integration or data cannot enter the available processing regime. It is equally unsuitable when success cannot be measured or when the system would be allowed to pay, delete, publish or decide about people without an independent barrier.
Sometimes the best application with AI integration has very little autonomy: the model extracts and explains, code validates, and a person decides. Maturity is not measured by how many actions the agent can perform, but by how carefully the forbidden actions have been selected.
Frequently asked questions
Is OpenAI Agents API the same as Agents SDK?
No. Agents API runs an OpenAI-managed Codex harness and preserves session progress. Agents SDK runs inside the developer's application and provides more direct control over orchestration, storage, approvals and runtime. Responses API remains the option closest to direct model calls.
Can an agent work without a sandbox?
Yes. If it uses only remote tools or functions supplied by the application, the environment may be set to “none”. A sandbox becomes necessary when it must run commands, work with files or produce artifacts in an execution space.
Can it directly modify a CRM or online store?
Only when the application exposes a function that permits the operation. Specific functions with validation and limited rights are safer, while sensitive operations should require confirmation. General database or administrator access is unnecessary.
Do subagents automatically improve the result?
No. They help with independent parallel tasks. For short or dependent stages, they add cost, latency and coordination. The benefit must be demonstrated through testing.
Is it ready for production now?
It is available in beta and can be evaluated in real projects with bounded impact. Critical workflows need fallbacks, monitoring and an acceptance that interfaces or limits may change.
The change that really matters
OpenAI Agents API reduces some of the infrastructure needed for long-running AI tasks that use several tools. That can shorten the path from prototype to a usable workflow. It does not shorten the work of understanding the process, cleaning data, designing permissions and testing exceptions.
The strongest applications will not be those promising total autonomy. They will give the agent enough freedom to handle genuine variation in work and little enough power that an error remains controllable. At that balance point, AI integration becomes useful software rather than an impressive demonstration that demands blind trust.
Verified official sources
- OpenAI Developers – Agents API overview, concepts and pricing
- OpenAI Developers – comparison of Agents API, Agents SDK and Responses API
- OpenAI Developers – harness, application and environment architecture
- OpenAI Developers – sandbox security and credential protection
- OpenAI Developers – subagents and multi-agent orchestration
- OpenAI Developers – tracing, usage and session debugging
Documentation and limitations were checked on 12 September 2026. Agents API is in beta, and technical options, pricing and data-processing terms should be verified again before implementation.